Explore our specialized services, tailored solutions, and industry expertise to elevate your digital presence. From custom WordPress development to seamless integrations, we build high-performing websites that deliver impact.
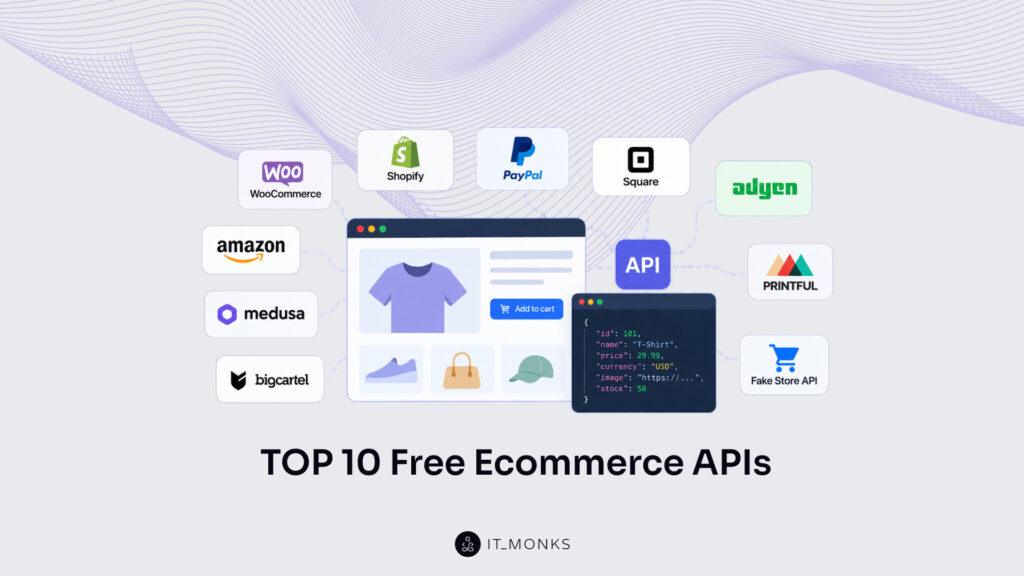
The 10 free ecommerce API options for 2026 are WooCommerce, Shopify, PayPal, Square, Adyen Checkout, Amazon Selling Partner API, Medusa, Big Cartel, Printful and Fake Store API: platform (including open-source headless), payment, marketplace, print-on-demand and mock APIs that connect a WordPress store, a hosted store or a test project to commerce data.
Free ecommerce APIs let startups, small stores, and developers build an integration with no upfront license fee: all 10 are free to call, open source, or offer a free plan or sandbox, with live-use fee models stated per entry. Any free ecommerce API still has to be chosen, connected through credentials, then run under security rules, rate limits and version changes. Choosing one starts with the data and actions an ecommerce API exposes.
What is an Ecommerce API?
An ecommerce API is an application programming interface that lets a store, app or service read and change ecommerce data through requests. The API exposes products, orders and payments as resources, each at its own endpoint address.
An app sends an HTTPS request to an endpoint; the API processes it, then returns JSON or performs an action, such as creating an order or capturing a payment.
Three jobs cover most ecommerce API traffic:
Product management: products, categories, attributes and inventory.
Order processing: orders, shipment tracking and returns.
Payment integration: payment gateways, payment methods and currencies.
In 2026, most ecommerce APIs are REST, with resources at versioned URLs, while the Shopify Admin API is GraphQL. Access mostly runs on OAuth 2.0 access tokens rather than static keys passed in a query string, and the account or plan behind that access decides what a store pays.
Benefits of Using Free Ecommerce APIs
The benefits of using free ecommerce APIs start with license cost: a free API puts no upfront software fee between a startup or small store and its first integration. Usage fees stay separate: payment APIs charge per transaction, hosted platforms charge per plan, and print-on-demand services charge per order. Beyond cost, an API adds a capability without a store rebuild, pre-built endpoints and SDKs shorten the build, and documentation answers integration questions.
Cost-effectiveness
Cost-effectiveness with free ecommerce APIs means building before paying. Open-source code from WooCommerce and Medusa, free developer accounts and sandboxes let a team build and test at no cost: the PayPal sandbox, the Square sandbox, an Adyen test account and Shopify development stores carry no charge. Billing starts with live trade. PayPal and Square charge per transaction, Printful charges per order, and none of the three bills per API call, so cost grows only as real sales arrive.
Flexibility and Scalability
Flexibility and scalability describe how far an ecommerce API lets a store grow without a rebuild. Payments, point of sale, print-on-demand and marketplace listing each arrive by connecting an API instead of rebuilding the store. Provider rate limits cap request volume where they exist, and on some platforms the cap rises with the plan, as Shopify’s query-cost points per second do. Within those limits, a developer adds each capability with the SDKs and sandboxes the provider ships.
Accelerated Development
Accelerated development with an ecommerce API comes from parts the provider has already built. Pre-built endpoints, official SDKs such as the Medusa JS SDK, and sandboxes cut build time, and the machine-readable OpenAPI spec from DummyJSON describes every endpoint in one file. Square also offers a Model Context Protocol (MCP) server, so AI coding assistants can call the API during the build. Each provider publishes reference documentation for these parts.
Community Support
Community support for an ecommerce API means the sources that answer integration questions without a support ticket. Official documentation, changelogs, developer forums and open-source SDK repositories document most of what a build runs into, from authentication errors to retired endpoints. WooCommerce and Medusa add one more source: as open source, their code has a contributor community around it. A team reads the documentation and changelog of every shortlisted API before choosing one.
Best Free Ecommerce APIs
The best ecommerce APIs for 2026 are WooCommerce REST API, the Shopify GraphQL Admin API with the Shopify Storefront API, PayPal REST APIs, Square APIs, Adyen Checkout API, Amazon Selling Partner API (SP-API), the Medusa Store and Admin APIs, Big Cartel API, Printful API and Fake Store API. “Free” across this ecommerce API list means one of three things: no fee to call the API, open-source code, or a free plan or sandbox for building and testing.
Where live selling or payments cost money, the entry names the fee model. Inclusion among the top ecommerce APIs requires four criteria: the API is free to use, the provider maintains it in 2026, keeps its documentation current and supports current authentication.
1. WooCommerce
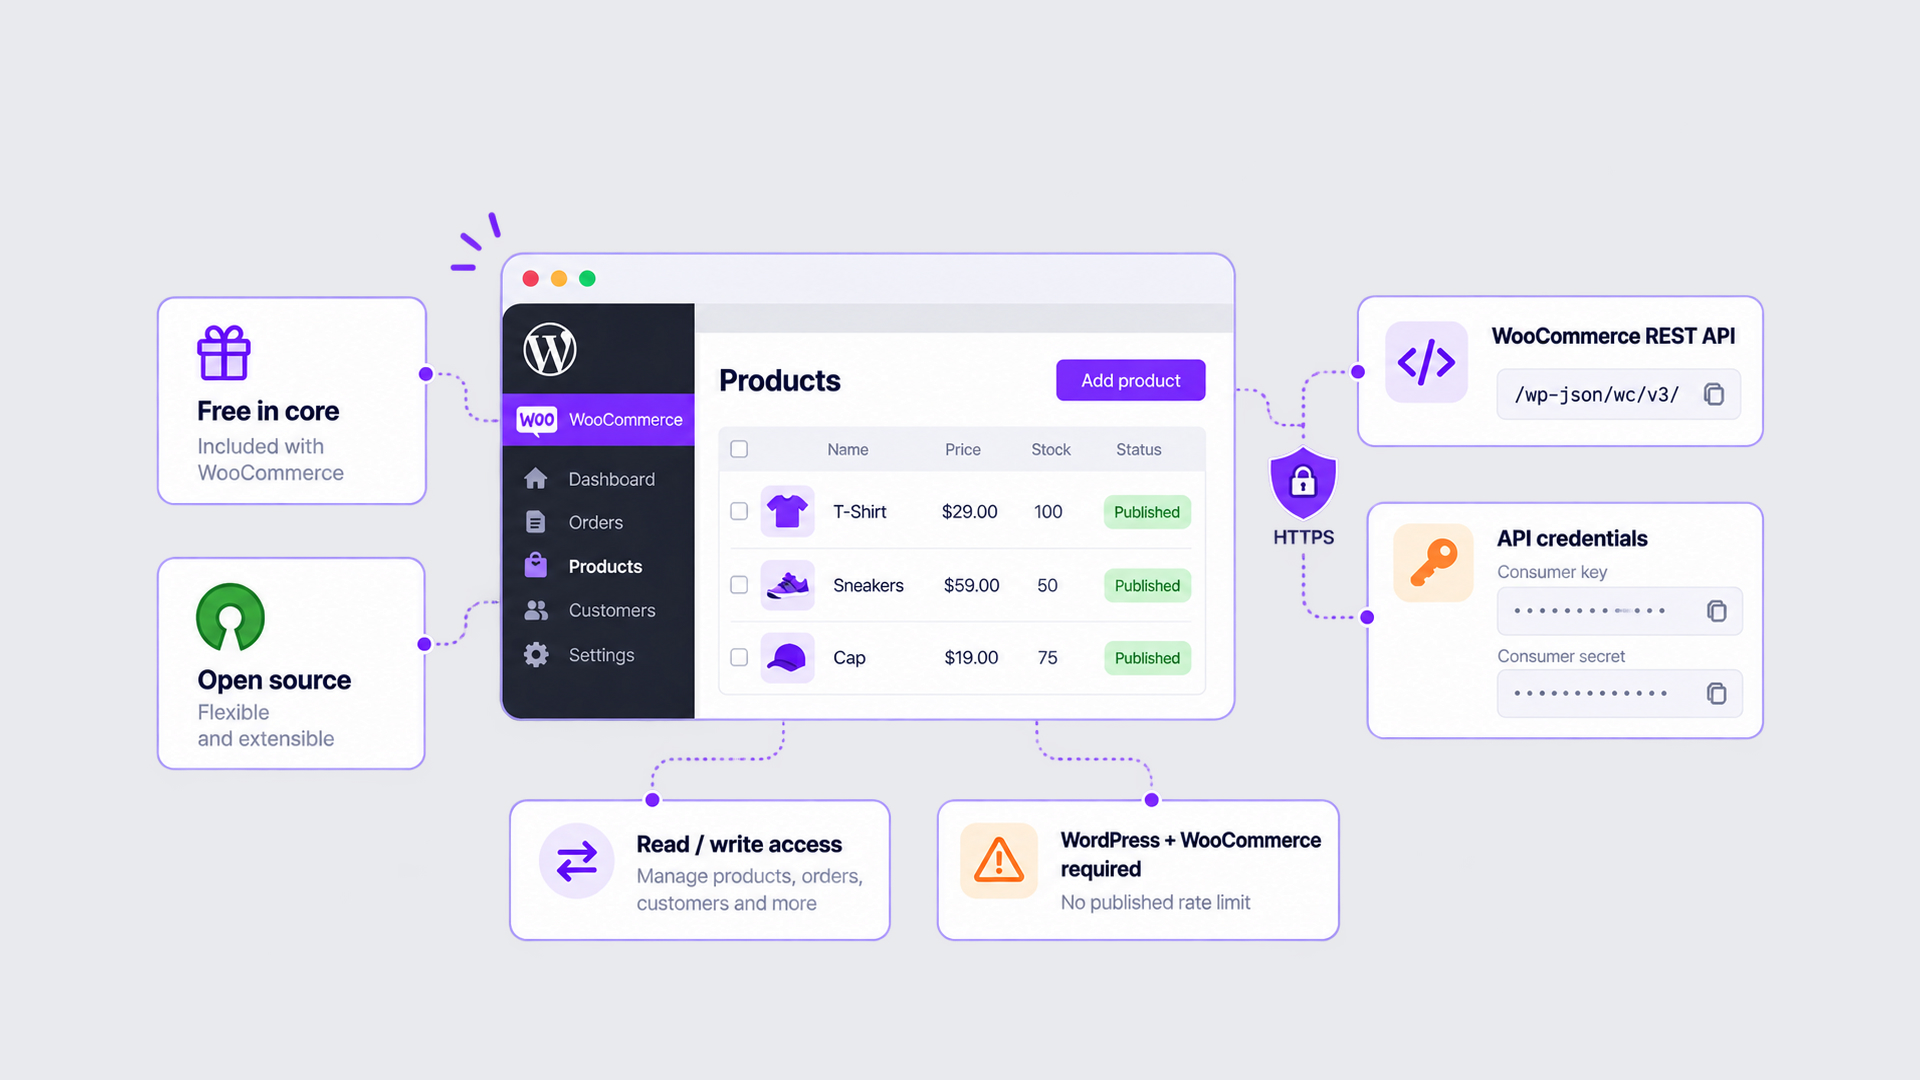
WooCommerce REST API is the open source ecommerce API built into the WooCommerce plugin for WordPress, and the API is free in core. It sits under its own namespace on top of the WordPress REST API, so its store endpoints share the /wp-json/ base with the rest of the site.
Features
REST API v3 at /wp-json/wc/v3/, the current version
Consumer key and consumer secret issued from WooCommerce > Settings > Advanced > REST API, with read or read/write access
HTTP Basic authentication over HTTPS; one-legged OAuth 1.0a over plain HTTP
Pretty permalinks enabled before the first call
Experimental Dual API offered only as a separate plugin, not for production
Strengths
Open source, with the core API free of charge
Runs inside WordPress, which makes it the default ecommerce API for WordPress stores
Regular releases across the WooCommerce 10.x and 11.x lines in 2026
Limitations
Requires WordPress plus the WooCommerce plugin (WordPress 4.4+ and WooCommerce 3.5+ for v3)
No published rate limit
Legacy REST API left core in WooCommerce 9.0 (June 2024) and survives only as a plugin
2. Shopify
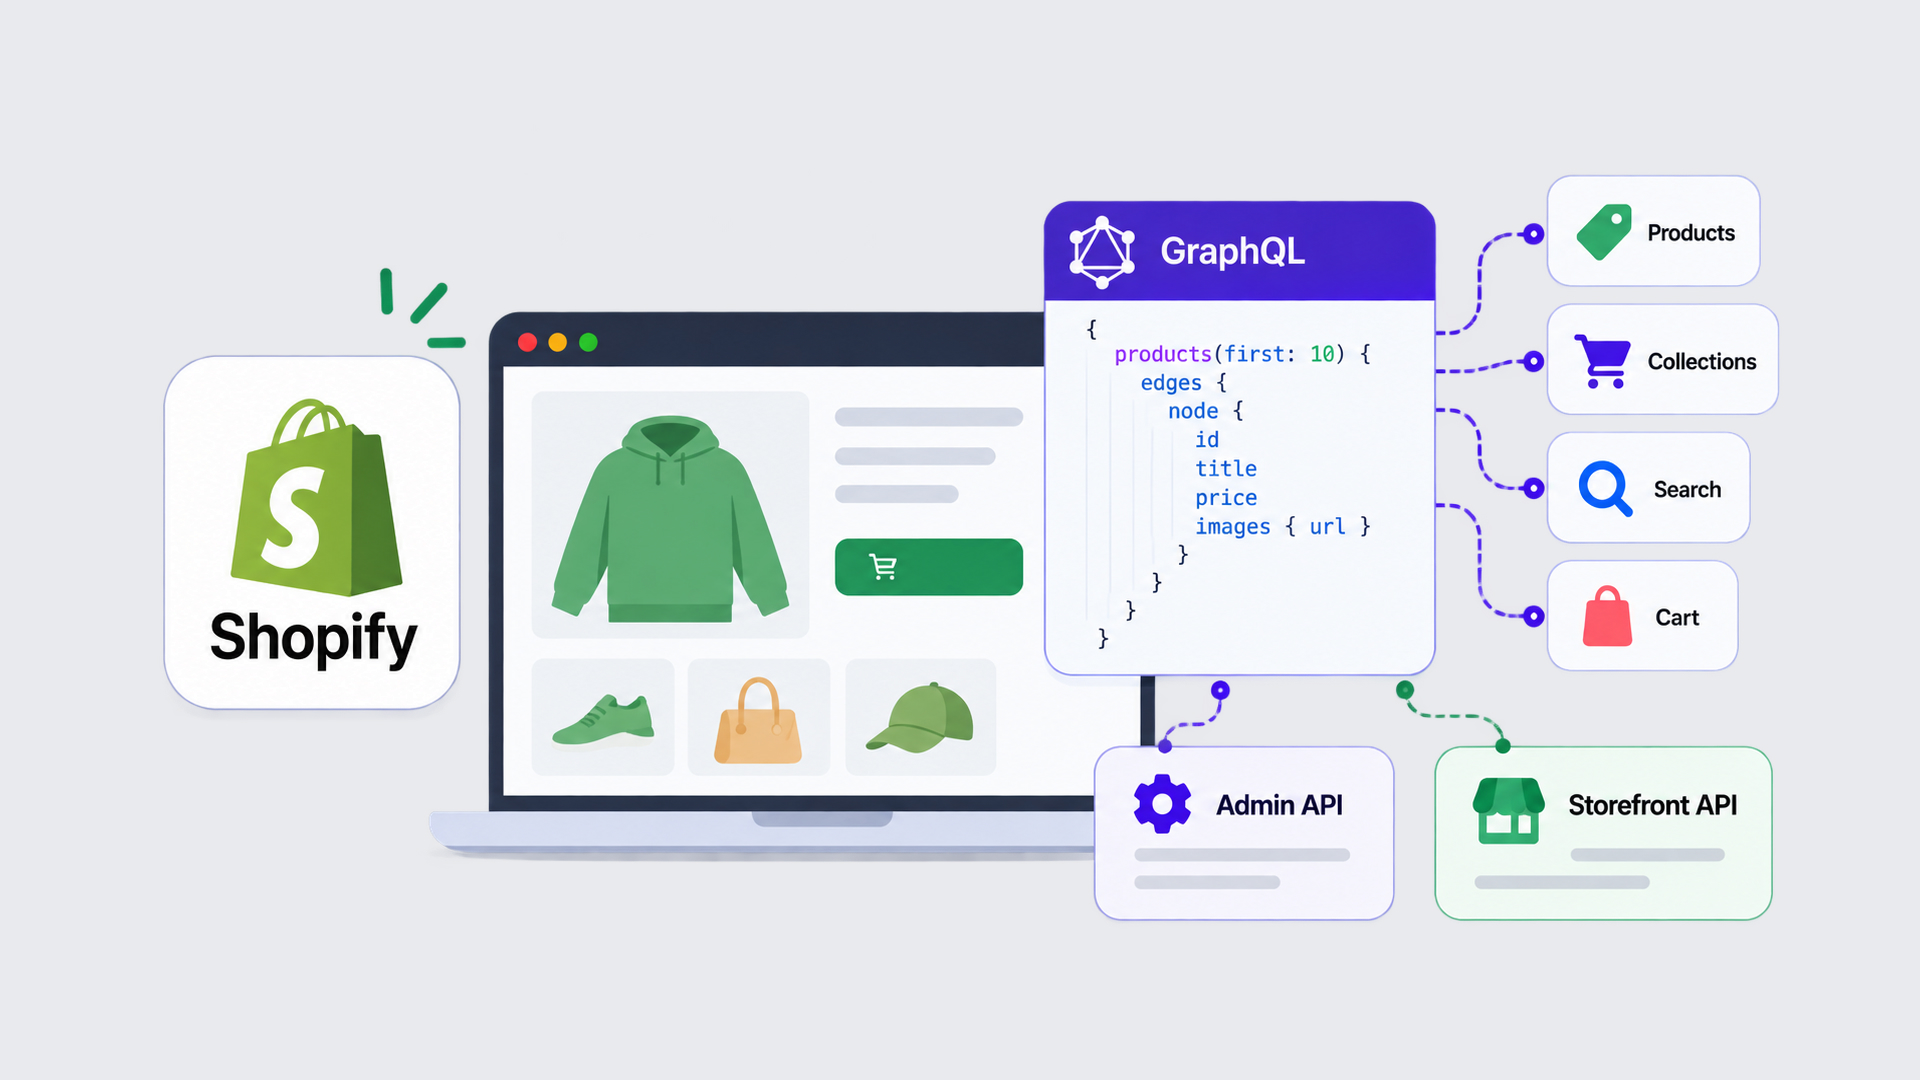
Shopify offers two GraphQL APIs for a hosted store: the Shopify GraphQL Admin API for store data, and the Shopify Storefront API for buyer-facing reads such as products, collections, search and cart. Both cost nothing to call, though a live store requires a paid Shopify plan. In the ecommerce REST API vs GraphQL contrast, REST exposes a fixed endpoint per resource, while GraphQL uses one endpoint and each query names the fields it wants back. Shopify marked its REST Admin API legacy in October 2024.
Features
Quarterly versions in YYYY-MM form, with 2026-10 as the latest stable version (supported to October 2027)
Admin access token issued when an app with set scopes is installed from the Dev Dashboard
Storefront API calls tokenless for products, collections, search and cart, or with a public or private token
One versioned GraphQL endpoint per API
Strengths
API access is free
Free development stores for building and testing
GraphQL returns only the fields a query names
Limitations
Selling requires a paid Shopify plan; development stores are test-only
New public apps require GraphQL since April 2025
Admin rate limits run from 100 to 2,000 query-cost points per second by plan: Standard 100, Advanced 200, Plus 1,000, Enterprise 2,000
3. PayPal
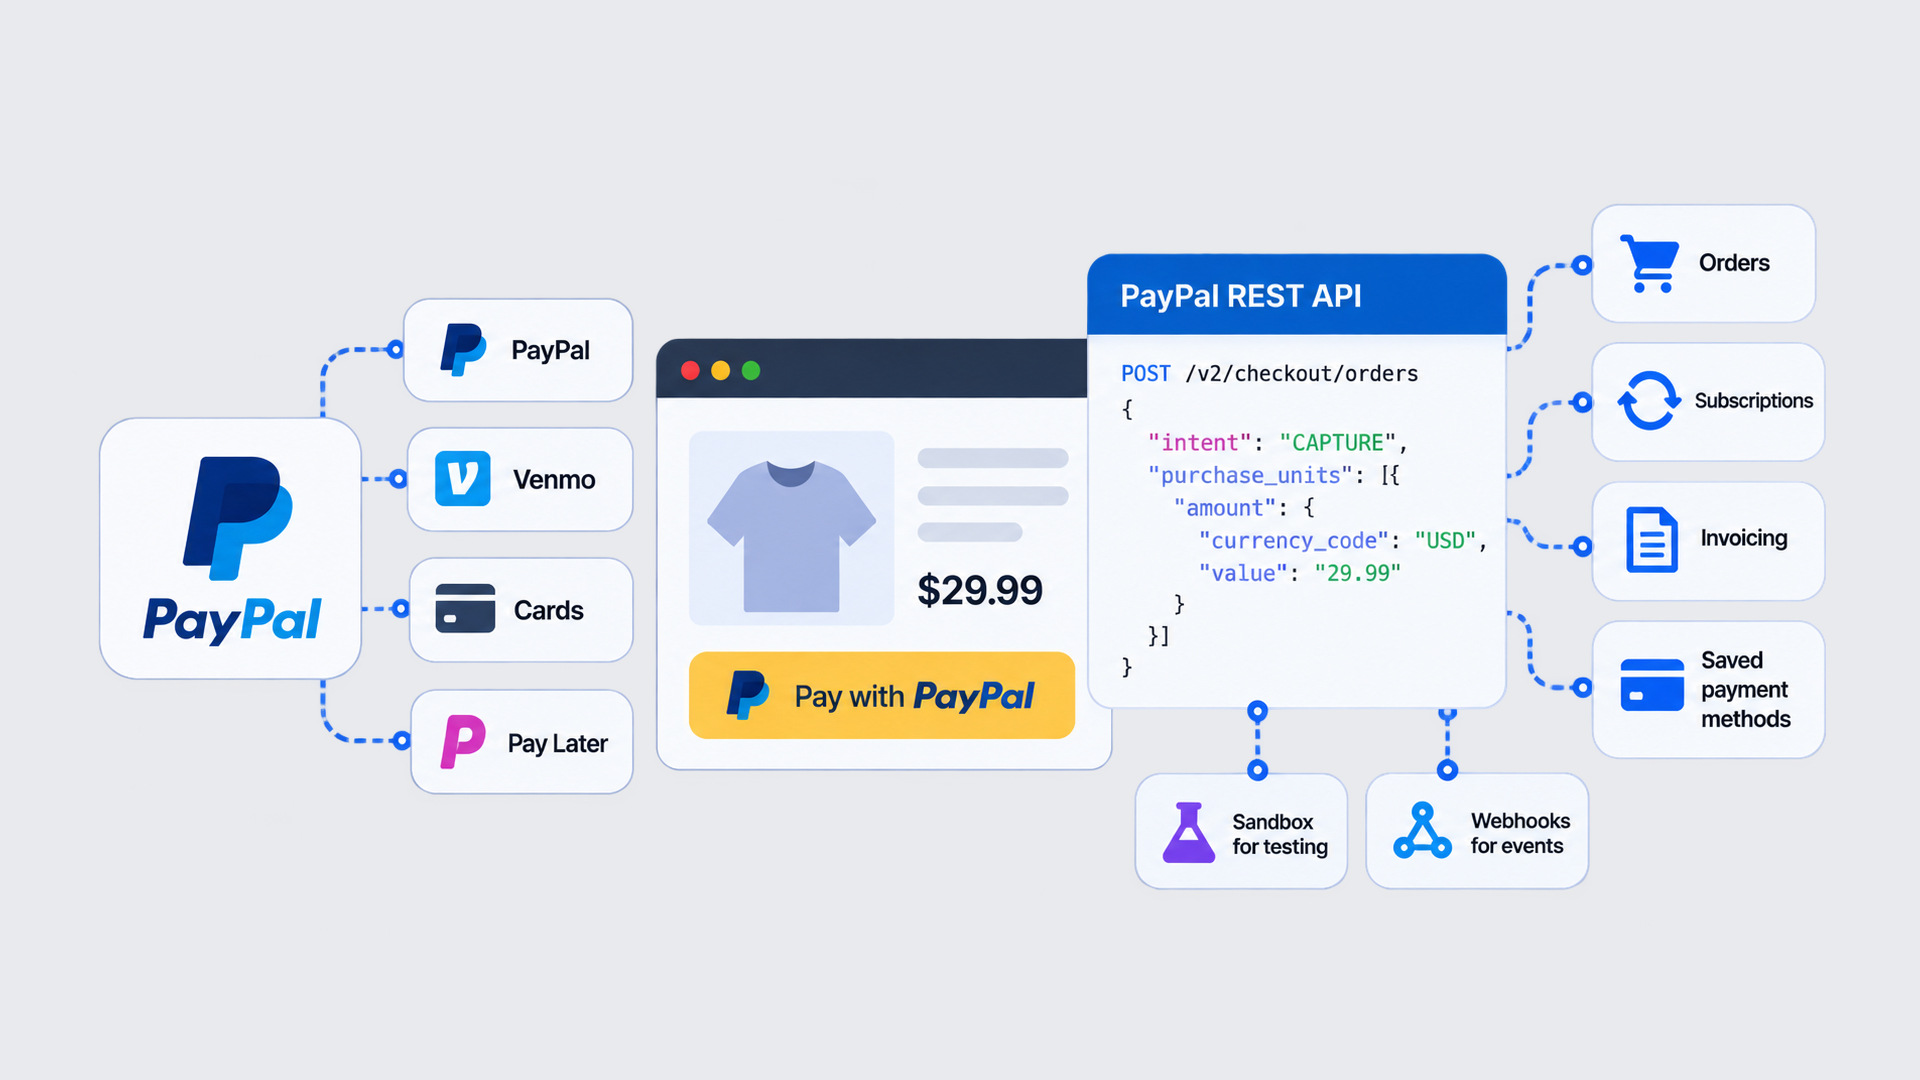
PayPal REST APIs are an ecommerce payment API family for orders, subscriptions, invoicing and saved payment methods, free to integrate and billed per transaction.
Features
Orders v2, Subscriptions, Invoicing and Vault v3 payment method tokens
Client ID and secret from Developer Dashboard > Apps & Credentials
Client ID and secret exchanged for an OAuth 2.0 access token, then sent as a bearer token on each API call
Default sandbox accounts for test payments
Webhooks for event notifications
Strengths
Free developer access and sandbox
PayPal, Venmo, cards and Pay Later through PayPal Open (February 2025)
Recurring billing through the Subscriptions API
Limitations
Transaction fees on every live payment, with an extra fee on international transactions
Going live requires a PayPal Business account
IPN is legacy; Webhooks replaced it for REST event notifications
4. Square API
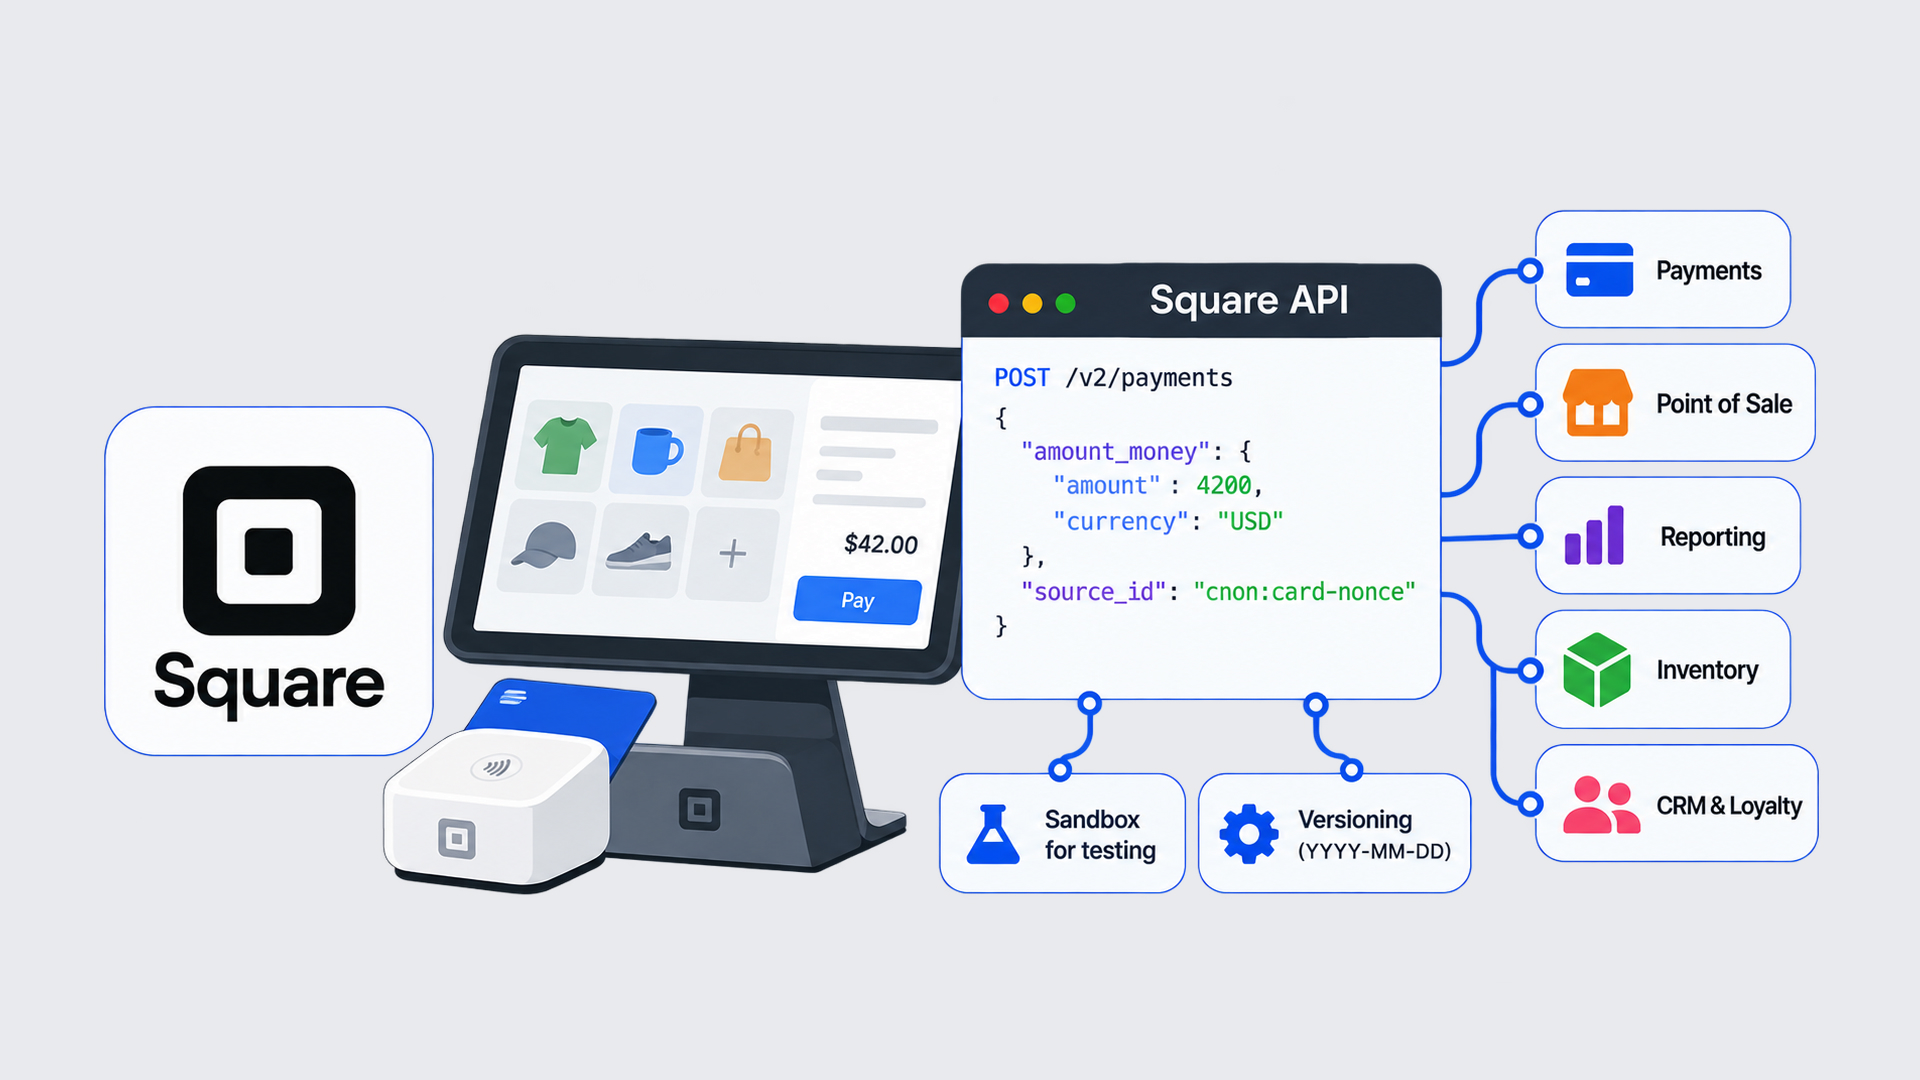
Square APIs are one API set for online and in-person commerce, available on the Square Free plan with no monthly fee and billed per transaction.
Features
Payments, point of sale, reporting, inventory, CRM and loyalty APIs
Personal access token for an owner’s own account; OAuth 2.0 code flow for apps, with PKCE for public apps and access tokens valid for 30 days
Square-Version header (YYYY-MM-DD) to pin every request to a tested version; retired endpoints return 410
Sandbox in the Developer Console, with the Web Payments SDK on the client and the Payments API on the server
Strengths
Square Free plan with no monthly fee and no long-term contract
Online and in-person sales in one account
Deprecation notice at least 12 months before an endpoint retires
Limitations
Transaction fees on every online, in-person and keyed-in payment
Throttled calls return 429 RATE_LIMITED, with no published request numbers
Version 2026-09-16 retired Transactions API writes in favor of the Payments and Refunds APIs
5. Adyen Checkout
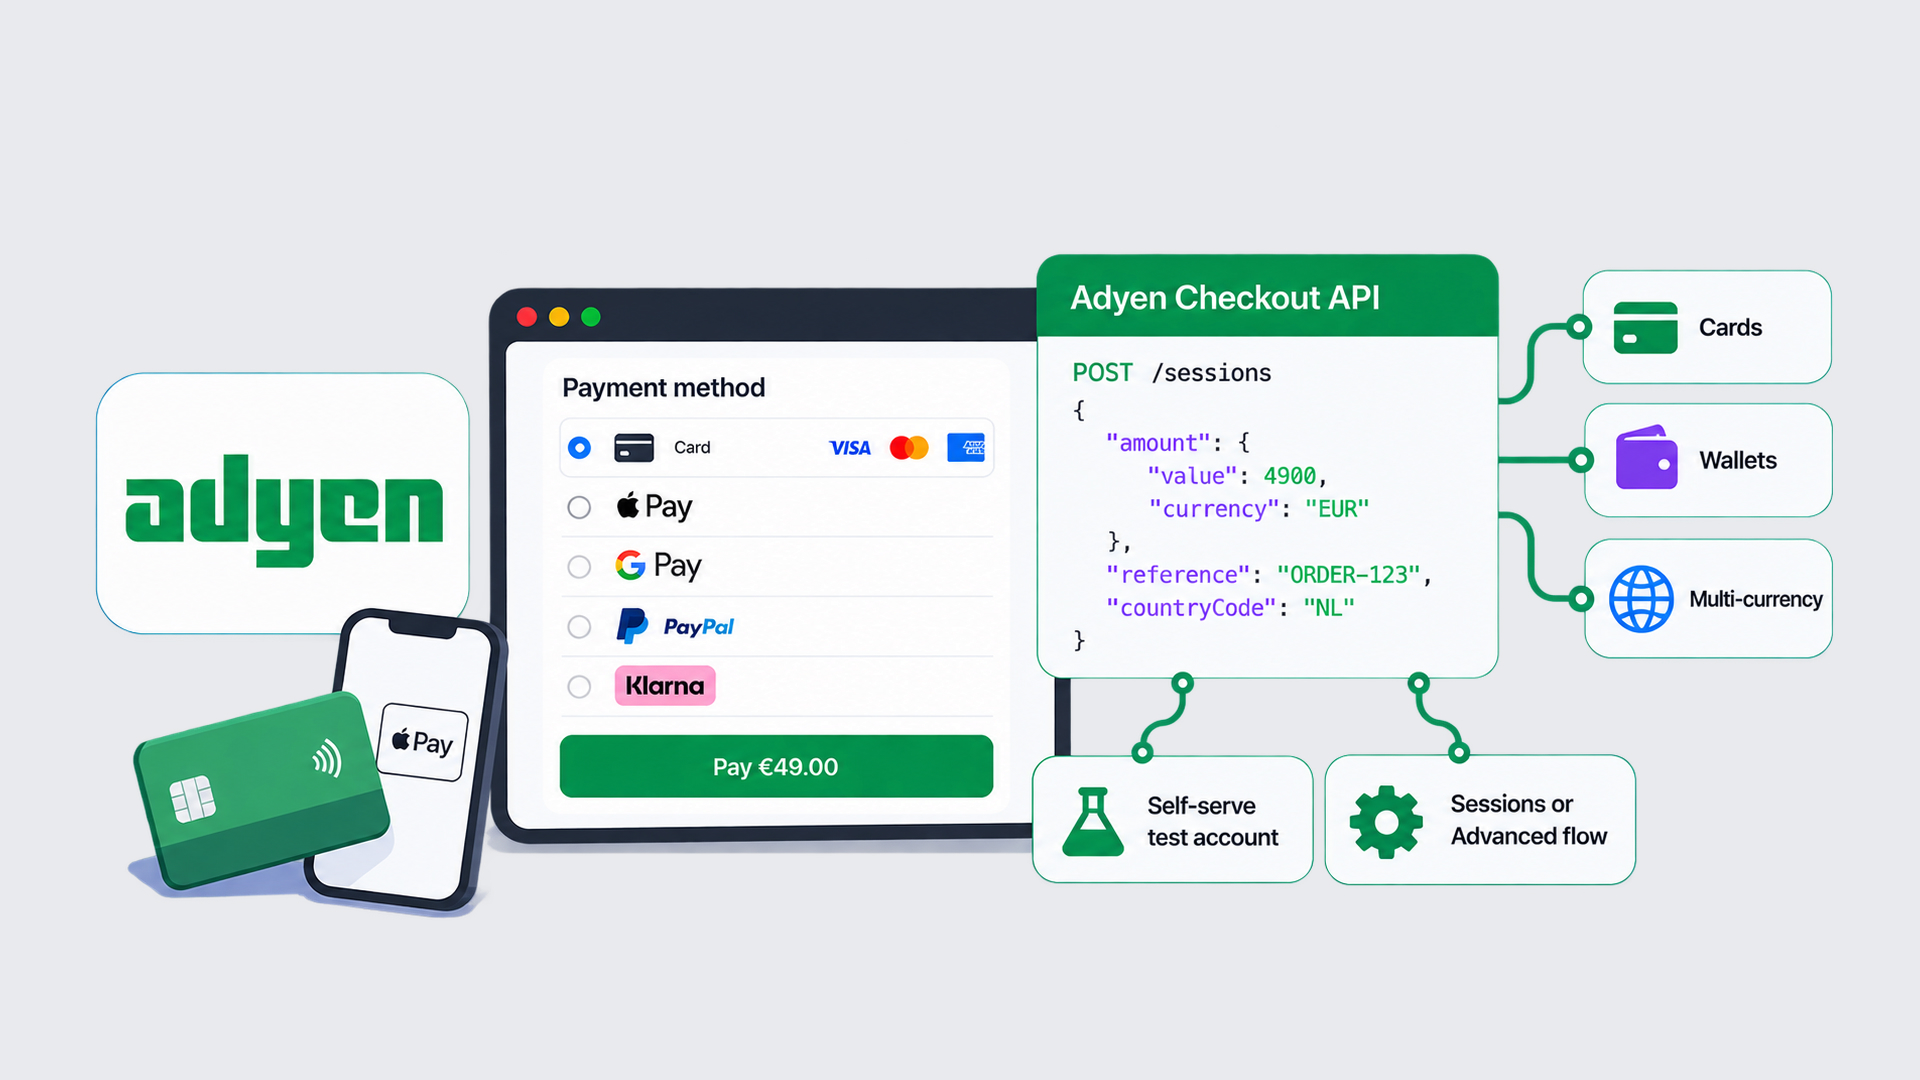
Adyen Checkout API is a payment API with a free self-serve test account and per-transaction pricing for live payments. The current version is v72 (April 2026).
Features
Checkout API v72, with Web Drop-in and Components v6 for the payment form
Server API key sent in the X-API-Key header
Client key (test_ or live_) bound to allowed origins
Sessions flow with one /sessions call, or Advanced flow across /paymentMethods, /payments and /payments/details
Strengths
No setup or monthly fee
Self-serve test account
Cards, wallets and multi-currency payments
Limitations
Minimum invoice that depends on industry, plus a per-transaction fee and a payment-method fee on live payments
Live account requires approval after an eligibility check
Advanced flow takes three calls per payment, against one in Sessions flow
6. Amazon API
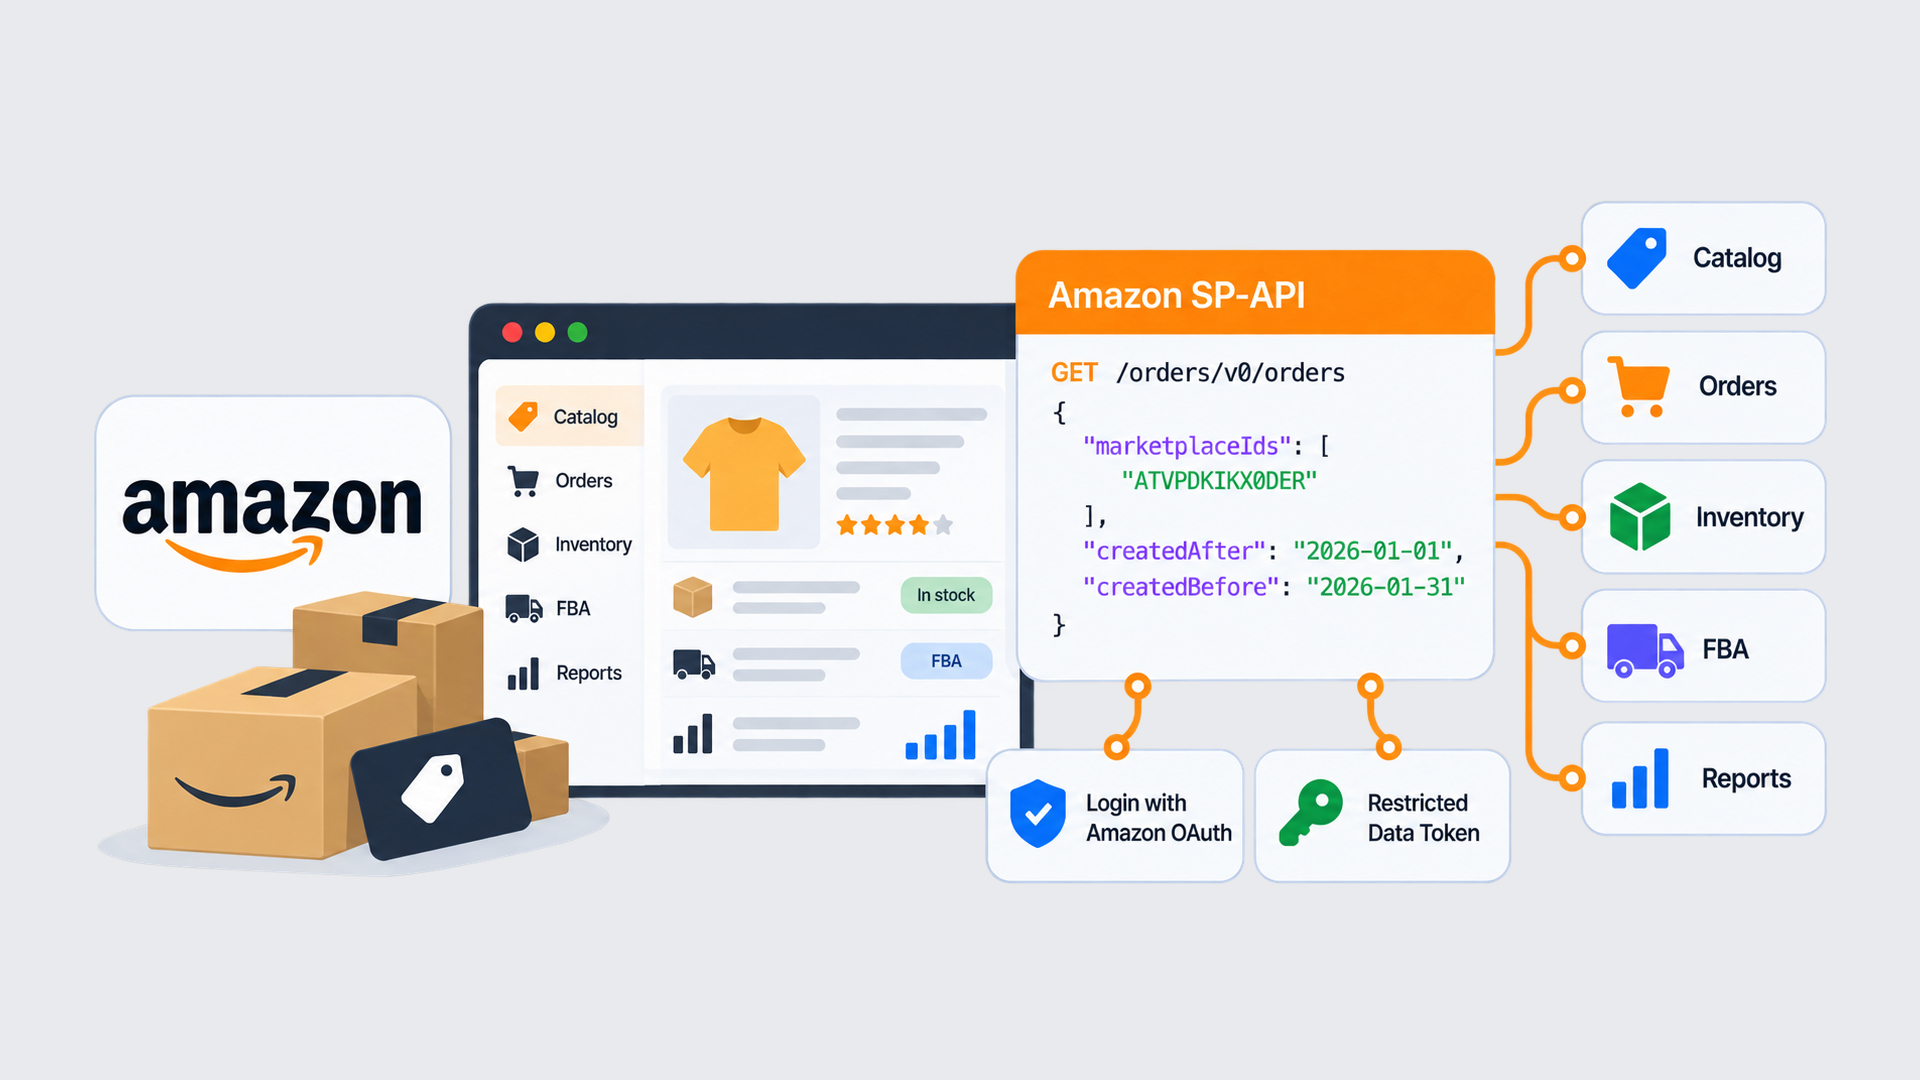
Amazon’s ecommerce API is the Amazon Selling Partner API (SP-API), a REST API for selling on Amazon that replaced MWS, removed on 1 April 2024. SP-API is free to developers; proposed developer fees were canceled in May 2026.
Features
SP-API sections for catalog, orders, inventory, FBA and reports, each versioned separately, mostly by date
Login with Amazon OAuth access token on every request
Restricted Data Token for calls that return personal data
Private apps self-authorized in Seller Central, or public apps listed in the Appstore after a security review
Strengths
Free to developers
No AWS IAM or Signature Version 4 since October 2023
One REST API for the core selling operations
Limitations
Private seller apps require a Professional selling account, billed as a monthly subscription plus selling fees, and every developer needs a profile in the Solution Provider Portal
Authorization renews every year, or sooner when roles change
Per-operation token-bucket usage plans set rate and burst, reported in the x-amzn-RateLimit-Limit header
7. Medusa
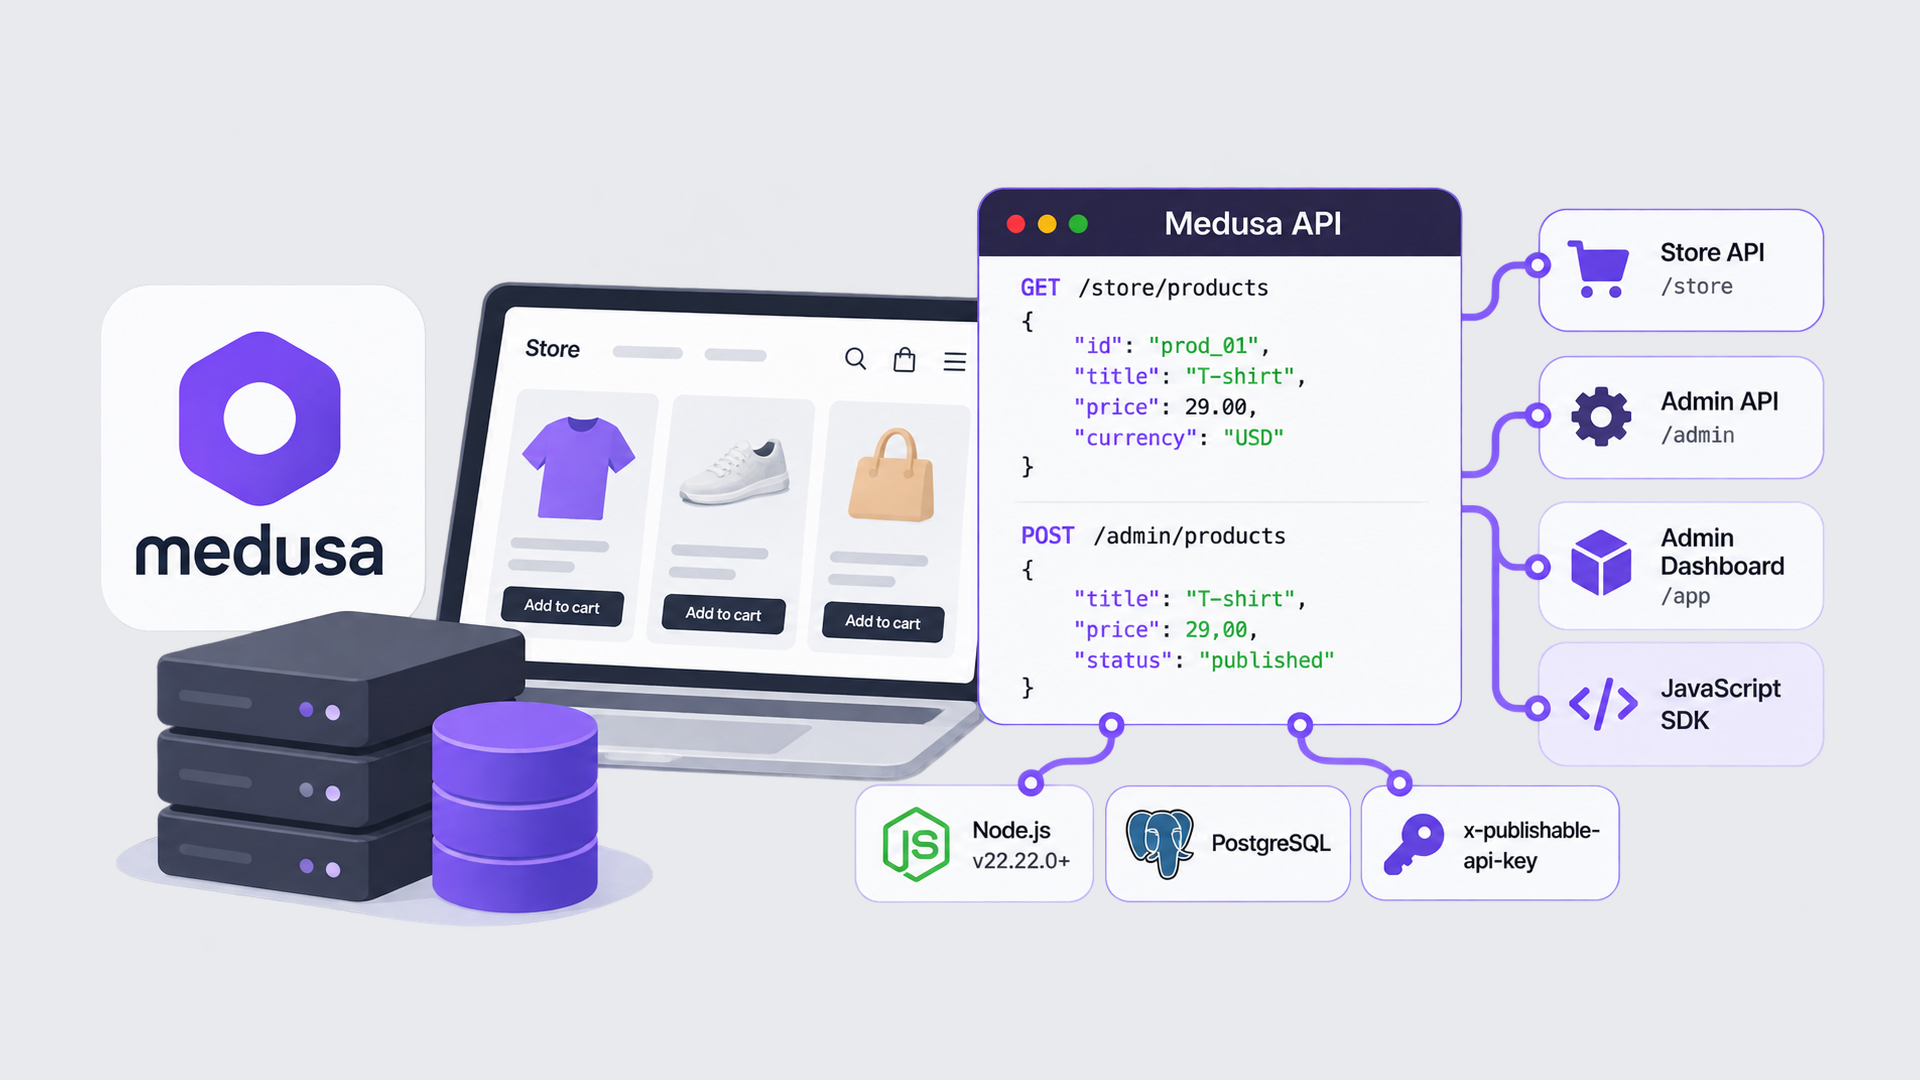
Medusa is an open-source headless commerce platform whose core is MIT-licensed and free to self-host. Its v2 line, latest release v2.22.1, exposes a Store API and an Admin API.
Features
Medusa Store API at /store for storefronts, Medusa Admin API at /admin for back office
JS SDK
Requires Node.js v22.22.0 or later LTS, Git and PostgreSQL; run npx create-medusa-app@latest
Server on port 9000, admin dashboard at /app
Publishable API key in the x-publishable-api-key header on Store API requests
Strengths
MIT-licensed core, free to self-host
JWT bearer token or cookie session for customers and admins
Secret API key for server-to-server Admin API calls
Limitations
Self-hosting: the store team runs the server and database
Medusa offers paid Medusa Cloud hosting and Enterprise Edition features
No published rate limits
8. Big Cartel
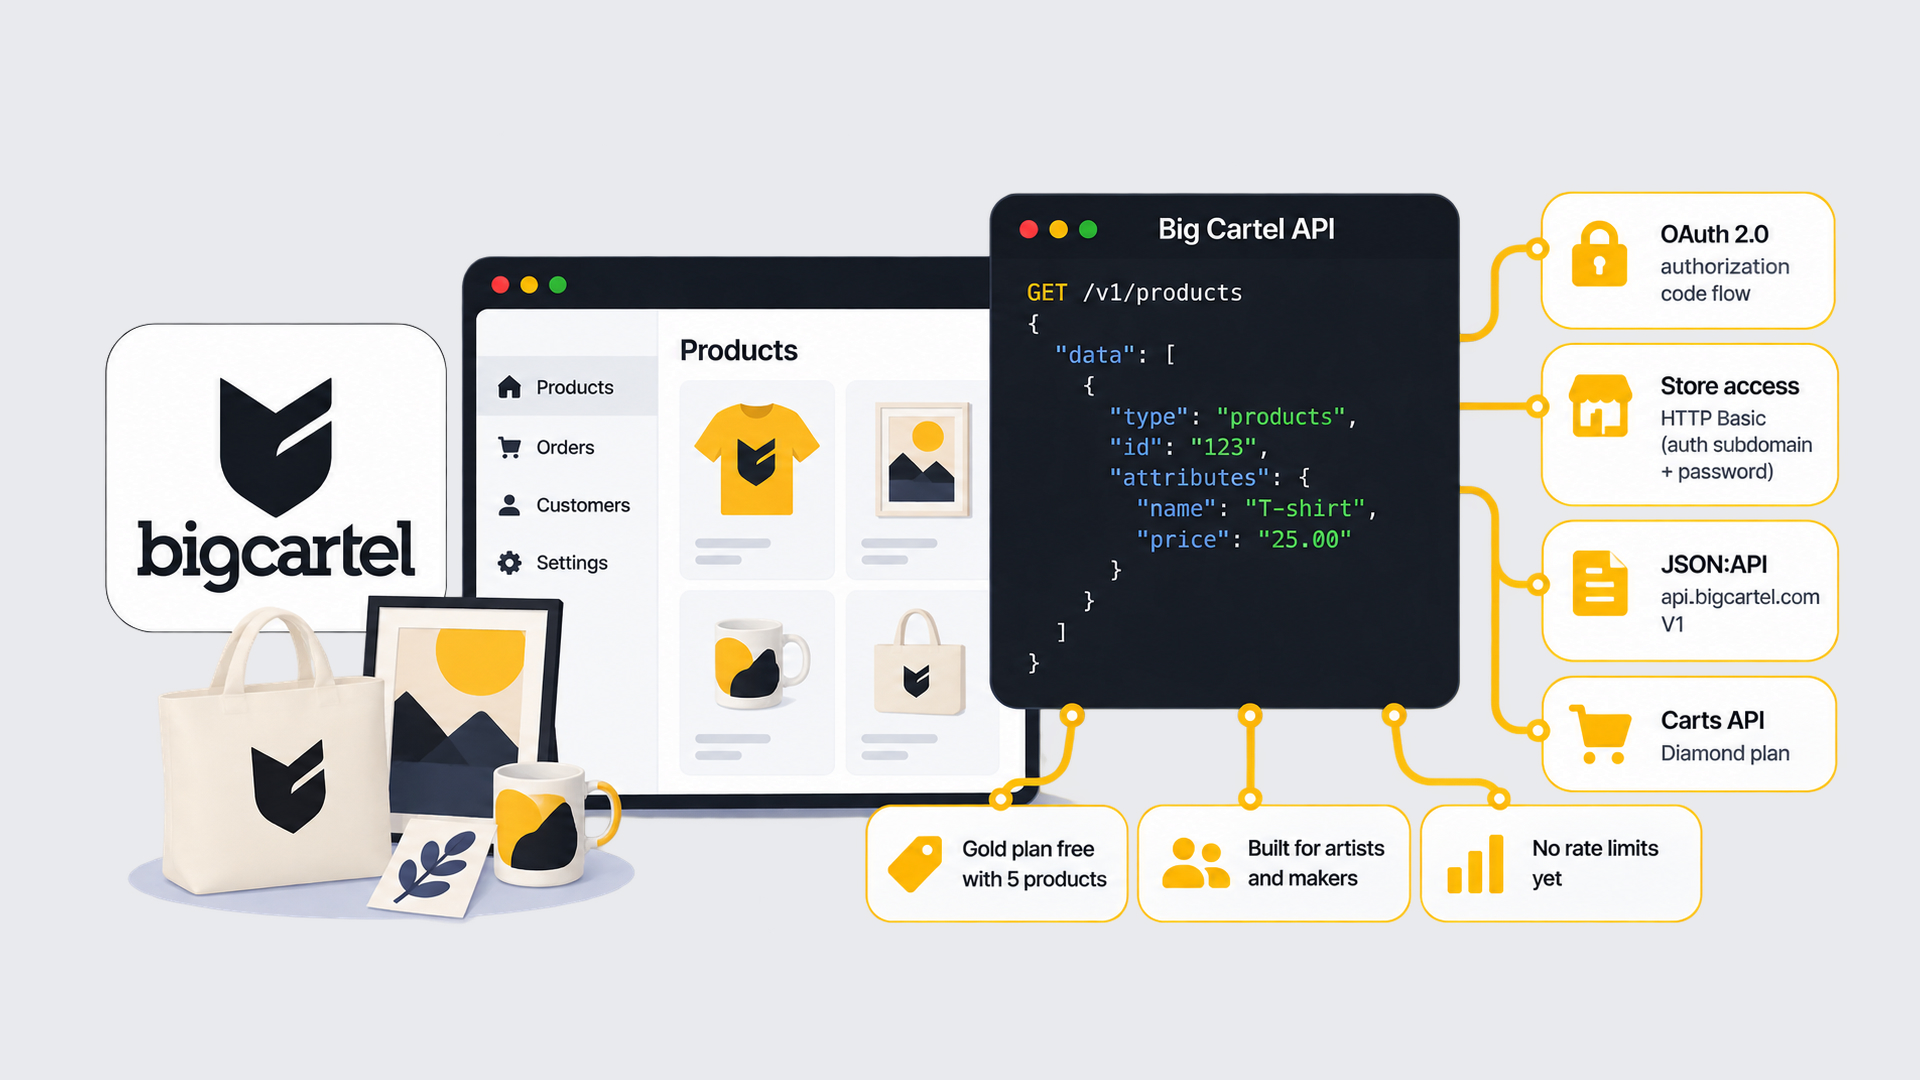
Big Cartel API is the API of a store platform for artists and makers, and the platform is free on the Gold plan with up to 5 products.
Features
Big Cartel API V1 at api.bigcartel.com, following the JSON:API specification
OAuth 2.0 authorization code flow for apps
HTTP Basic with store subdomain and password for an owner’s own store
Required headers: Accept application/vnd.api+json and a descriptive User-Agent
Strengths
Gold plan free with 5 products
Built for small creative stores
No rate limits yet, though Big Cartel states they will be added
Limitations
Public apps require an approved developer application and an API license agreement, granted to a select number of partners and developers
Carts API requires the paid Diamond plan
Product caps per plan: 5 products on Gold, raised on paid monthly Platinum and Diamond plans
9. Printful
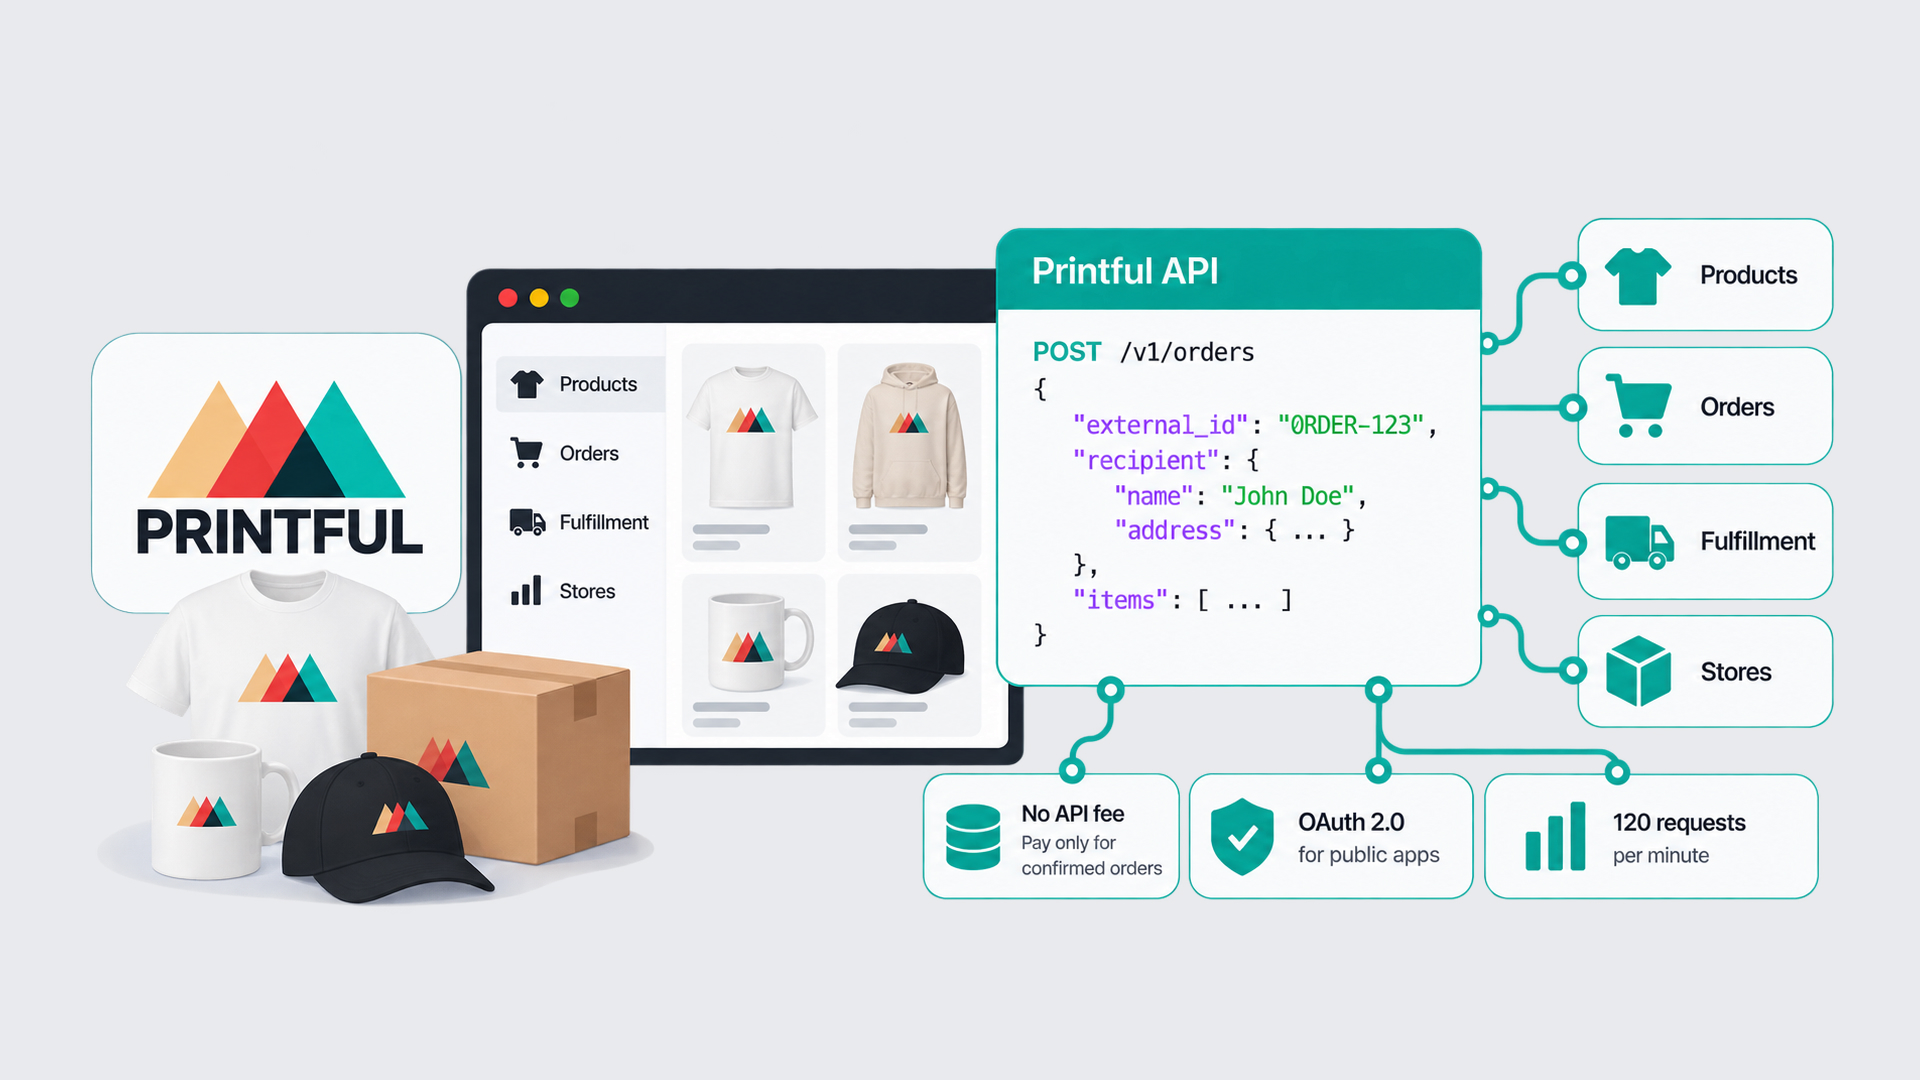
Printful API is a print-on-demand API with no API fee: Printful bills a store only for confirmed orders. Orders, products and fulfillment all run through the same API.
Features
v1 stable; v2 in open beta
Private token sent as a Bearer token for an owner’s own store
OAuth 2.0 for public apps, with access tokens valid for 1 hour and refresh tokens for 90 days
X-PF-Store-Id header with account-level tokens
Strengths
No API fee; charges apply only to confirmed orders
Token scopes limit each app to the data it needs
v2 usable in production during its open beta
Limitations
Rate limits of 120 requests per minute in general and 10 per minute for product sync
Requests over the limit return 429 with a Retry-After header
Unauthenticated calls capped at 30 requests per minute
10. Fake Store API
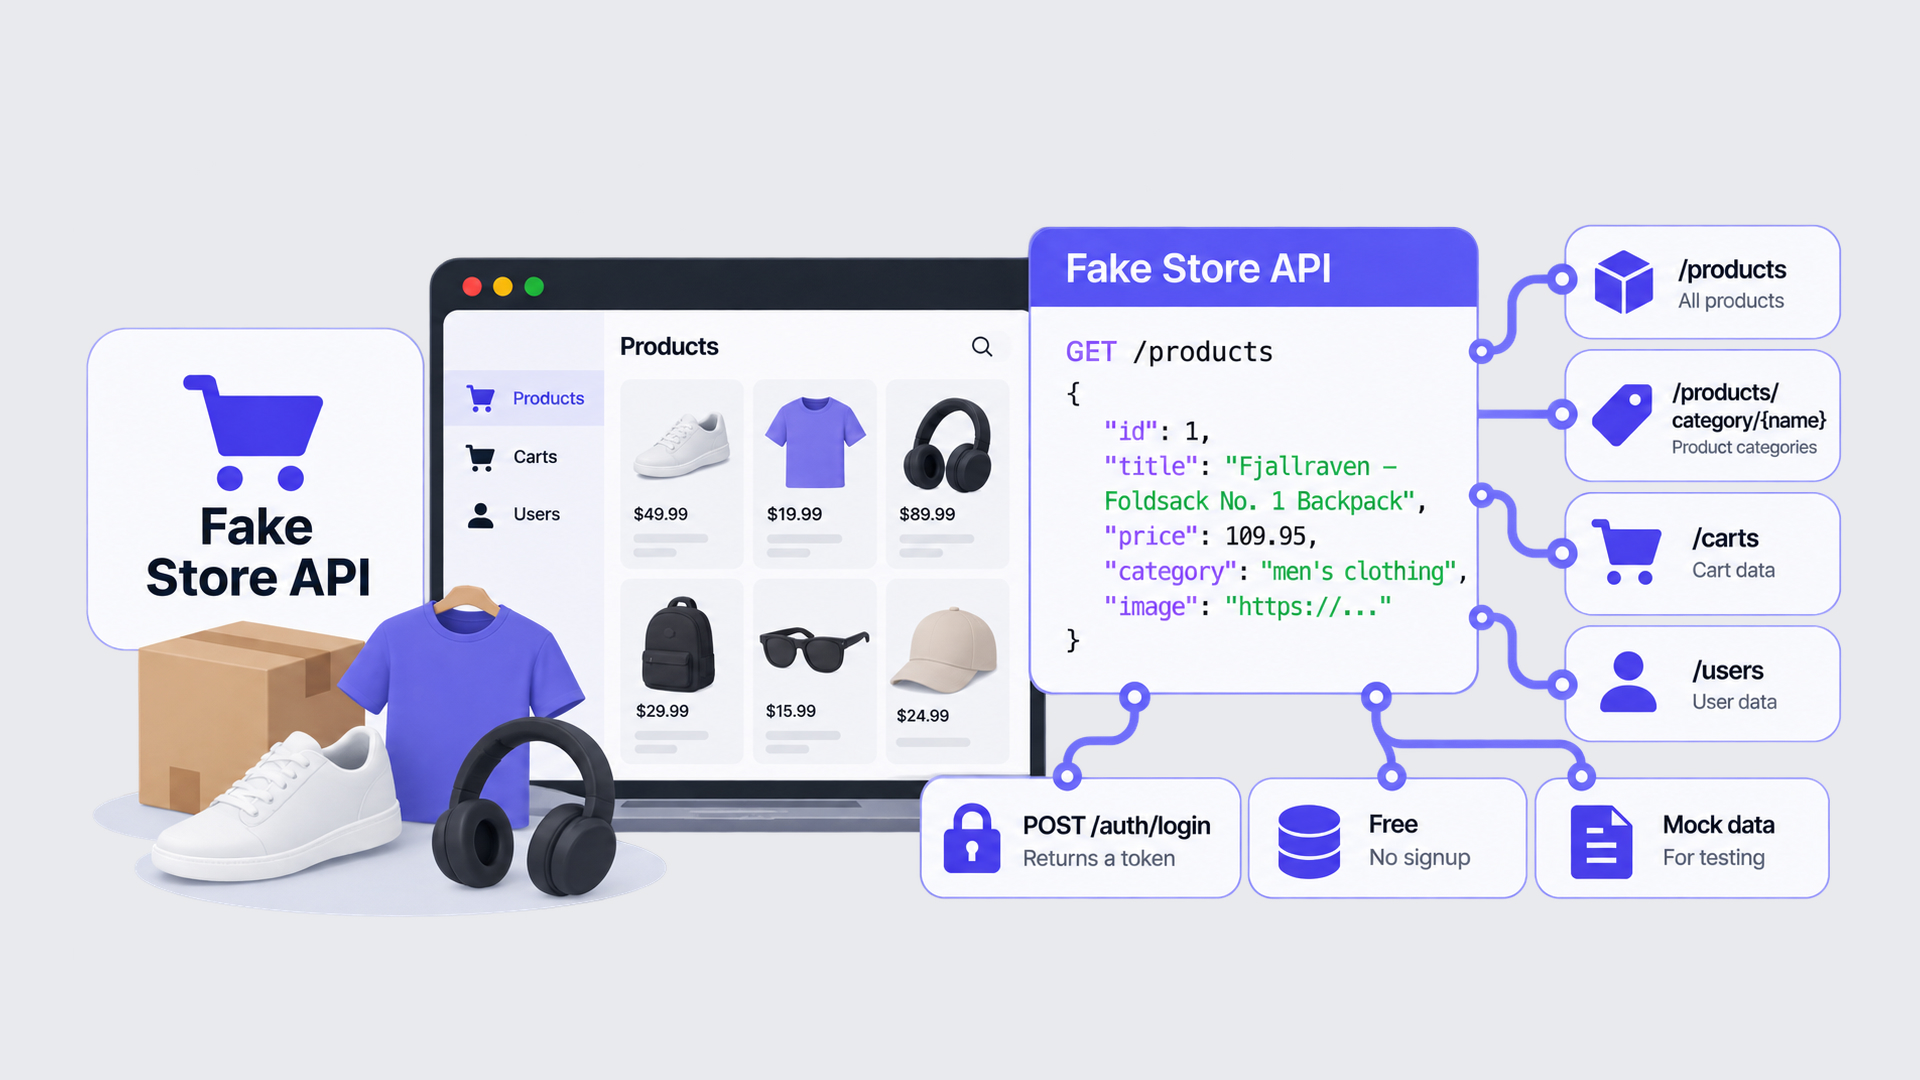
Fake Store API is a free mock REST API, an ecommerce API for testing rather than selling: it serves dummy product, cart and user data with no signup. DummyJSON is the larger dummy ecommerce API alternative, with 194 products and JWT login that returns a refresh token.
Features
/products, /carts and /users endpoints
Categories at /products/categories, filtered at /products/category/{name}
POST /auth/login returns a token
No key for reads
Strengths
Free, no signup
Ready product data for prototypes and front-end tests
Simple REST paths
Limitations
Writes are simulated, not saved
Small, fixed data set of products, carts and users
Not for production
A prototype that works against the mock API still needs a live provider, chosen on requirements and connected with real keys.
How to Get Started with a Free Ecommerce API
Getting started with a free ecommerce API is a three-stage sequence: choose the API, get credentials and make a first request, then integrate it into the store.
Step-by-Step Guide on How to Choose the Right API
An ecommerce API comparison is a four-step selection process: define requirements, research the available APIs, evaluate performance and reliability, then test the shortlist. That order lets a development team rule out a poor fit before anyone registers for keys.
Step 1: Identify Your Requirements
Requirements are what the ecommerce API must do for the store: catalog, orders, payments or fulfillment functions, on a given store platform and stack. Compare expected request volume with each candidate’s published rate limits. Then decide the client type: an app that stores a secret server-side suits a confidential flow, while a browser or mobile app needs a public-client flow.
Step 2: Research Available APIs
Researching available APIs means checking four things per candidate: documentation, changelog, official SDKs and the auth model, usually OAuth 2.0 or a static key. A dated changelog shows how much notice a deprecation gets. For a payment API, confirm support for PCI DSS v4.0.1, published in June 2024.
Step 3: Evaluate Performance and Reliability
Performance and reliability are measured by status pages and uptime history, latency from the store’s region, and published rate limits. Printful allows 120 requests per minute on general endpoints; Shopify’s GraphQL Admin API counts query-cost points per second, 100 on the Standard plan. Where no limit number is published, plan for 429 Too Many Requests responses.
Step 4: Test the API
Testing an API runs in the provider’s sandbox, before any live key exists: PayPal sandbox accounts, a Square sandbox token, an Adyen self-serve test account, a free Shopify development store, a local Medusa install. For front-end mock data, Fake Store API and DummyJSON need no key. An API that passes its sandbox tests is ready for live credentials.
How to Get API Keys and Start Making Requests
API keys are the credentials an ecommerce API issues to identify the app behind each request. Most ecommerce APIs in 2026 issue OAuth 2.0 credentials, a client ID and a client secret, rather than one static key.
PayPal exchanges the client ID and secret directly for an access token; Square, Big Cartel, Amazon SP-API and Printful public apps first need the merchant to authorize the app, then exchange the authorization code for a token. Square and Printful also issue a personal or private token for an owner’s own store. Getting ecommerce API credentials and making a first request takes five steps:
Register a developer account with the provider.
Create an app in the developer dashboard.
Copy the client ID and secret, or the API key where the provider issues one.
Exchange the credentials, or the merchant’s authorization code, for an access token.
Send the token as Authorization: Bearer over HTTPS on each request.
The PayPal sandbox shows the full exchange in two calls. The first returns a bearer token; the second creates an order with it and returns the order ID.
Static keys remain at WooCommerce (a consumer key and secret), Adyen (an API key in the X-API-Key header) and Medusa (a secret API key for the Admin API). A key belongs in a query string only where the API requires it. WooCommerce sends its key pair through HTTP Basic auth over HTTPS, the same transport WordPress application passwords use for WordPress REST API authentication. Whatever the scheme, restrict scopes, and lock keys to allowed IPs or origins where the provider offers it. Once sandbox requests carrying the token return 200, the credentials are ready for integration.
How to Integrate API into Your Existing Ecommerce Platform
Integrating an API into an existing ecommerce platform is a five-step sequence from SDK choice to monitoring: official SDKs, code practices, key security, testing and usage monitoring. The SDK decision shapes the code around it, so it comes first.
Step 1: Use Official SDKs and Libraries
Official SDKs and libraries are the client packages a provider publishes for its own API; use one where it exists. Medusa ships a JS SDK for its Store and Admin APIs, while Square’s Web Payments SDK builds the client-side payment form beside the Payments API on the server. An SDK handles auth headers and request formatting; pin the API version it targets, such as a Square-Version date. Raw HTTP still suits small calls.
Step 2: Follow Best Practices
Best practices for integration code start with structure: a modular API client, central error handling, and structured logging of each request and response status. For order and payment events, subscribe to webhooks instead of polling. PayPal’s REST APIs report those events through Webhooks, the same push model behind WordPress webhooks on the store side.
Step 3: Secure Your API Keys
Securing API keys starts with storage: environment variables or a secret manager, never client code or a code repository. Give each key the narrowest scope that works, or a restricted key where offered. Separate keys per service contain a leak, and rotating credentials on every staff change closes old access. Two keys are public by design: Adyen client keys, locked to allowed origins, and Medusa publishable API keys.
Step 4: Test Thoroughly
Thorough testing of an integration covers two layers. Unit tests check request building and every error path. End-to-end flows then run in the sandbox with the provider’s test cards: a successful payment, a decline, a refund and webhook delivery for each event.
Step 5: Monitor API Usage
API usage monitoring tracks request volume, error rate and latency per provider. Read rate-limit headers where the API sends them, such as Amazon SP-API’s x-amzn-RateLimit-Limit. Alert on 429 and 5xx spikes and on usage approaching a quota, so throttling shows up on a dashboard before it shows up as lost orders. With monitoring in place, the integration moves into daily operation.
Best Practices for Using Ecommerce APIs
Best practices for using ecommerce APIs are the operating habits that keep an ecommerce API integration running after launch. They come down to four: security, rate-limit and error handling, documentation kept within reach, and tracking versions before old ones are deprecated.
Security Considerations
Security considerations for an ecommerce API start with one habit: treat every key and access token as a password. Send credentials over HTTPS only, and keep stored secrets encrypted.
RFC 9700, the OAuth 2.0 Security Best Current Practice published in January 2025, requires PKCE for public clients and recommends it for confidential ones. The implicit grant should not be used; the resource owner password grant must not be. Access tokens should be sender-constrained through mutual TLS or DPoP, and public clients must sender-constrain or rotate refresh tokens, so a leaked token loses most of its value.
A valid token proves identity, not permission. Broken object-level authorization ranks first in the OWASP API Security Top 10 (2023), so the server must check, on every request, that the authenticated caller owns the order, customer or cart it asks for. Payment flows sit under PCI DSS v4.0.1, the version that replaced v4.0 at the end of 2024. Even a secured, authorized caller still works within the provider’s request quotas.
Rate Limiting and Handling API Response Errors
Rate limiting is the practice of capping how many requests an ecommerce API provider accepts per time window; past that cap, the API returns an error instead of data. Every response carries a status code: RFC 9110 groups the codes into classes, and four of them plus one throttling code shape error handling:
2xx: success.
3xx: redirection.
4xx: client error; fix the request.
5xx: server error; retry if transient.
429 Too Many Requests (a 4xx code): throttled; wait for Retry-After.
The 429 code comes from RFC 6585, while its Retry-After header, defined in RFC 9110, states how long to pause. Retry 429 and transient 5xx responses with exponential backoff and a retry cap. Failed 4xx validation requests, resent unchanged, return the same error.
Providers meter in their own units: Shopify counts query cost in points per second, Amazon’s SP-API applies a token bucket per operation, and Square returns RATE_LIMITED. On a WordPress store, the same status classes are the starting point to fix WordPress REST API errors. Where a status code alone does not explain a failure, the provider’s documentation does.
Keeping the API Documentation Handy for Troubleshooting
API documentation for troubleshooting means three resources kept at hand: the versioned reference that matches the pinned version (such as the Medusa Store and Admin API references), the changelog, and any OpenAPI spec or API explorer the provider publishes, such as the Adyen API Explorer. When a call fails, rerun the provider’s own example request first. If that request succeeds, the fault sits in the integration code, not in the ecommerce API.
Staying Updated with API Version Changes and Updates
API version changes reach an ecommerce API integration through three versioning styles: a version number in the path (PayPal /v2, WooCommerce wc/v3, Adyen v72), a release date in the path (Shopify 2026-10, released quarterly and supported for at least 12 months), and a date header (Square-Version).
Old versions do get retired. Amazon removed MWS in April 2024 in favor of SP-API, and WooCommerce 9.0 took the Legacy REST API out of core in June 2024. Square version 2026-09-16 retired Transactions API writes, replaced by the Payments and Refunds APIs; retired endpoints return 410.
Pin every version explicitly. Read changelogs on each release cycle, and test upgrades in staging before production traffic reaches a deprecated endpoint.
Conclusion
The 10 free-to-use ecommerce APIs cover five store needs: platform (WooCommerce, Shopify, Big Cartel, open-source headless Medusa), payment (PayPal, Square, Adyen), marketplace (Amazon), print-on-demand (Printful) and test data (Fake Store API). Transaction, plan, order and other fees apply only where an entry names them, and running any of these APIs well depends on current auth, pinned versions and rate-limit handling.
The choice that suits a store follows its platform and order volume. Connecting that API to everything else is integration work: IT Monks integrates CRMs, payment gateways, geolocation services, cloud platforms and messaging systems, whether a team plans to create an ecommerce website with WordPress or needs to sync an existing store.


 ChatGPT
 Claude
 Grok
 Gemini